
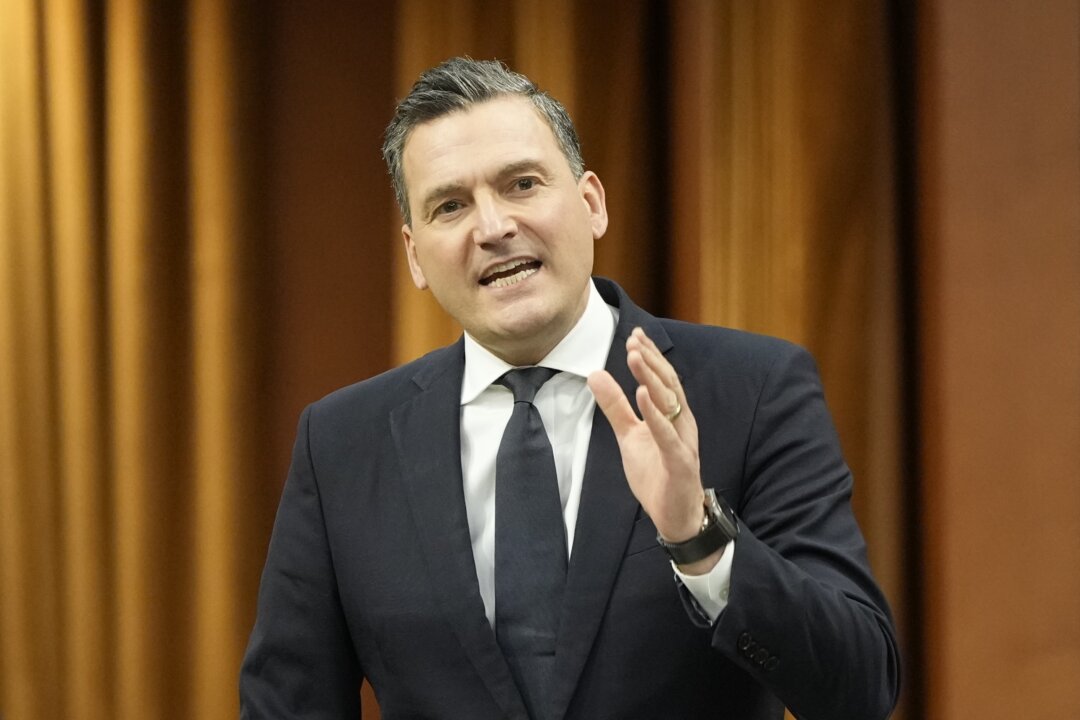
Artificial Intelligence and Digital Innovation Minister Evan Solomon rises during question period on Parliament Hill in Ottawa on June 15, 2026. The Canadian Press/Adrian Wyld
Canada’s artificial intelligence minister says Ottawa has temporarily taken some federal websites offline to protect government systems and Canadians’ information from an identified security risk.
Artificial Intelligence Minister Evan Solomon said in an Oct. 21 social media post that Ottawa took the precautionary measure on the advice of the Canadian Centre for Cyber Security after experts identified a vulnerability in PHP, software widely used to power websites.
“This is a global issue, and other governments and organizations are also taking protective measures,” he said, while encouraging organizations that use PHP to apply the latest security updates quickly and follow the Cyber Centre for updates.
Solomon said the federal government would restore affected websites once patches were applied. He did not mention which specific websites were taken offline.
The United States’ Federal Bureau of Investigation’s cyber division said the vulnerability could allow malicious actors to remotely execute code in the PHP programming language, potentially compromising sensitive data and networks.
Cybersecurity officials have said that roughly 70 percent of all websites on the internet use PHP. WordPress, Wikipedia, Etsy, Tumblr, Facebook, and Flickr are among the popular sites that use the language.
Meanwhile, the PHP Foundation, which includes developers who work on securing the programming language, said it released fixes for the vulnerabilities, along with instructions on how to update systems.
PHP developers said on Oct. 20 that they identified two critical vulnerabilities and stressed that users should immediately update their sites.
Huntress, a cybersecurity company that monitors security breaches, warned that information about the two vulnerabilities surfaced online before their scheduled disclosure and before patches were available. In an Oct. 21 update, the company said it had not observed exploitation among its partners as of 10 a.m. ET, although other organizations were reporting emerging attacks. It urged website operators to install the security updates as soon as possible.
“PHP is everywhere. It quietly powers WordPress, Drupal, Joomla, and Magento sites, shared hosting platforms, control panels, and an awful lot of software that doesn’t even advertise that it runs PHP under the hood,” Huntress said in a blog post.
“When a critical bug lands in PHP itself, rather than in one app built on top of it, the number of places you have to go looking to identify vulnerable PHP versions gets very big, very fast.”
It’s not clear how the details of the PHP vulnerability were released before the fix went live. But cybersecurity company watchTowr said on X that it could confirm that the detail release was real, and that users should “take this seriously and apply patches when available.”
The Canadian Press contributed to this report.

 English (US) ·
 Turkish (TR) ·
